Your SCAP™
Activation Toolkit.
Everything you need to launch a whole-of-supply-chain cyber assurance program — from contract clauses and supplier comms to real-time verification. Built to run independently or alongside your CyberCert dashboard.
Enterprise-supported
Enterprise-supported
What This Toolkit Gives You.
A complete, ready-to-deploy activation pack for primes managing supplier cyber risk at scale.
Program Setup Guide
Phased rollout plan — from supplier segmentation to ongoing assurance. Run it independently or with a CyberCert implementation partner.
Tier Classification
Clear supplier segmentation — Tier 1 enterprise vs Tier 2 SMB, with risk-mapped certification requirements for High, Medium, and Low risk suppliers.
Contract Clauses
Ready-to-insert procurement clauses with the 2-tier supplier model. Risk-based requirements mapped to Bronze through Diamond certification levels.
Email Templates
Full communication flow — initial announcement, reminders, escalation, and confirmation. Separate flows for Silver and Gold+ requirements.
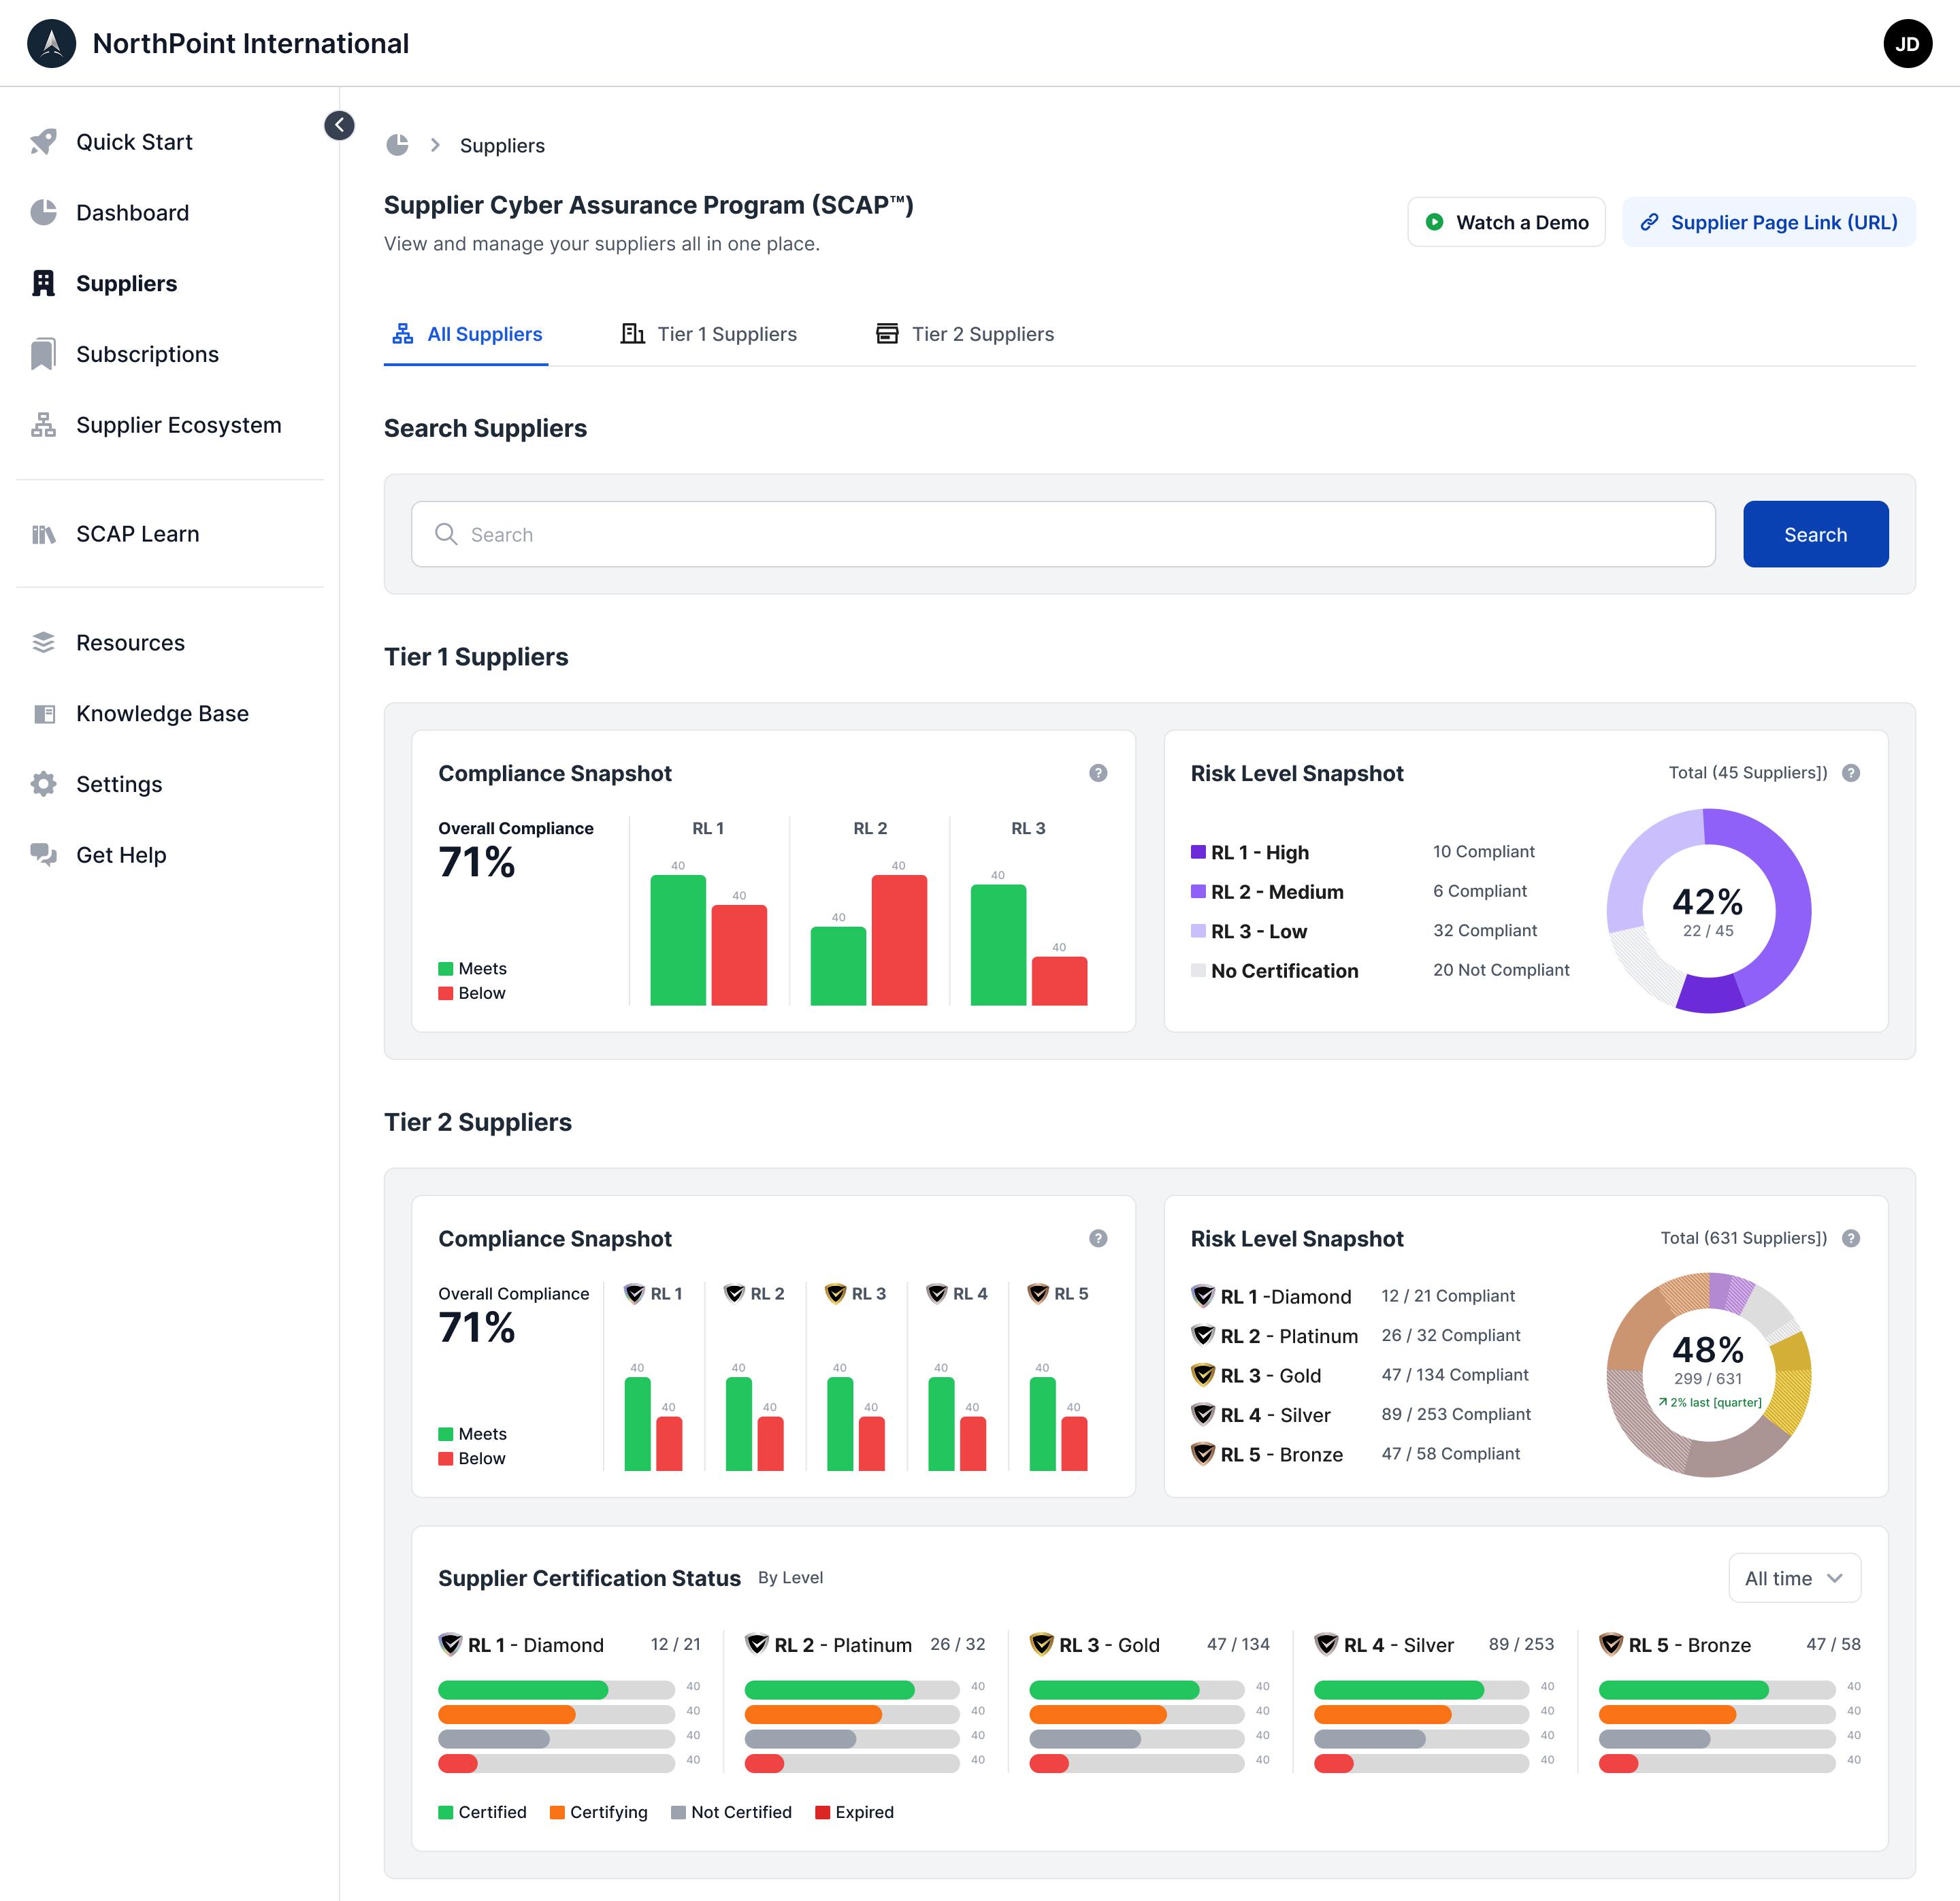
Tracking Tools
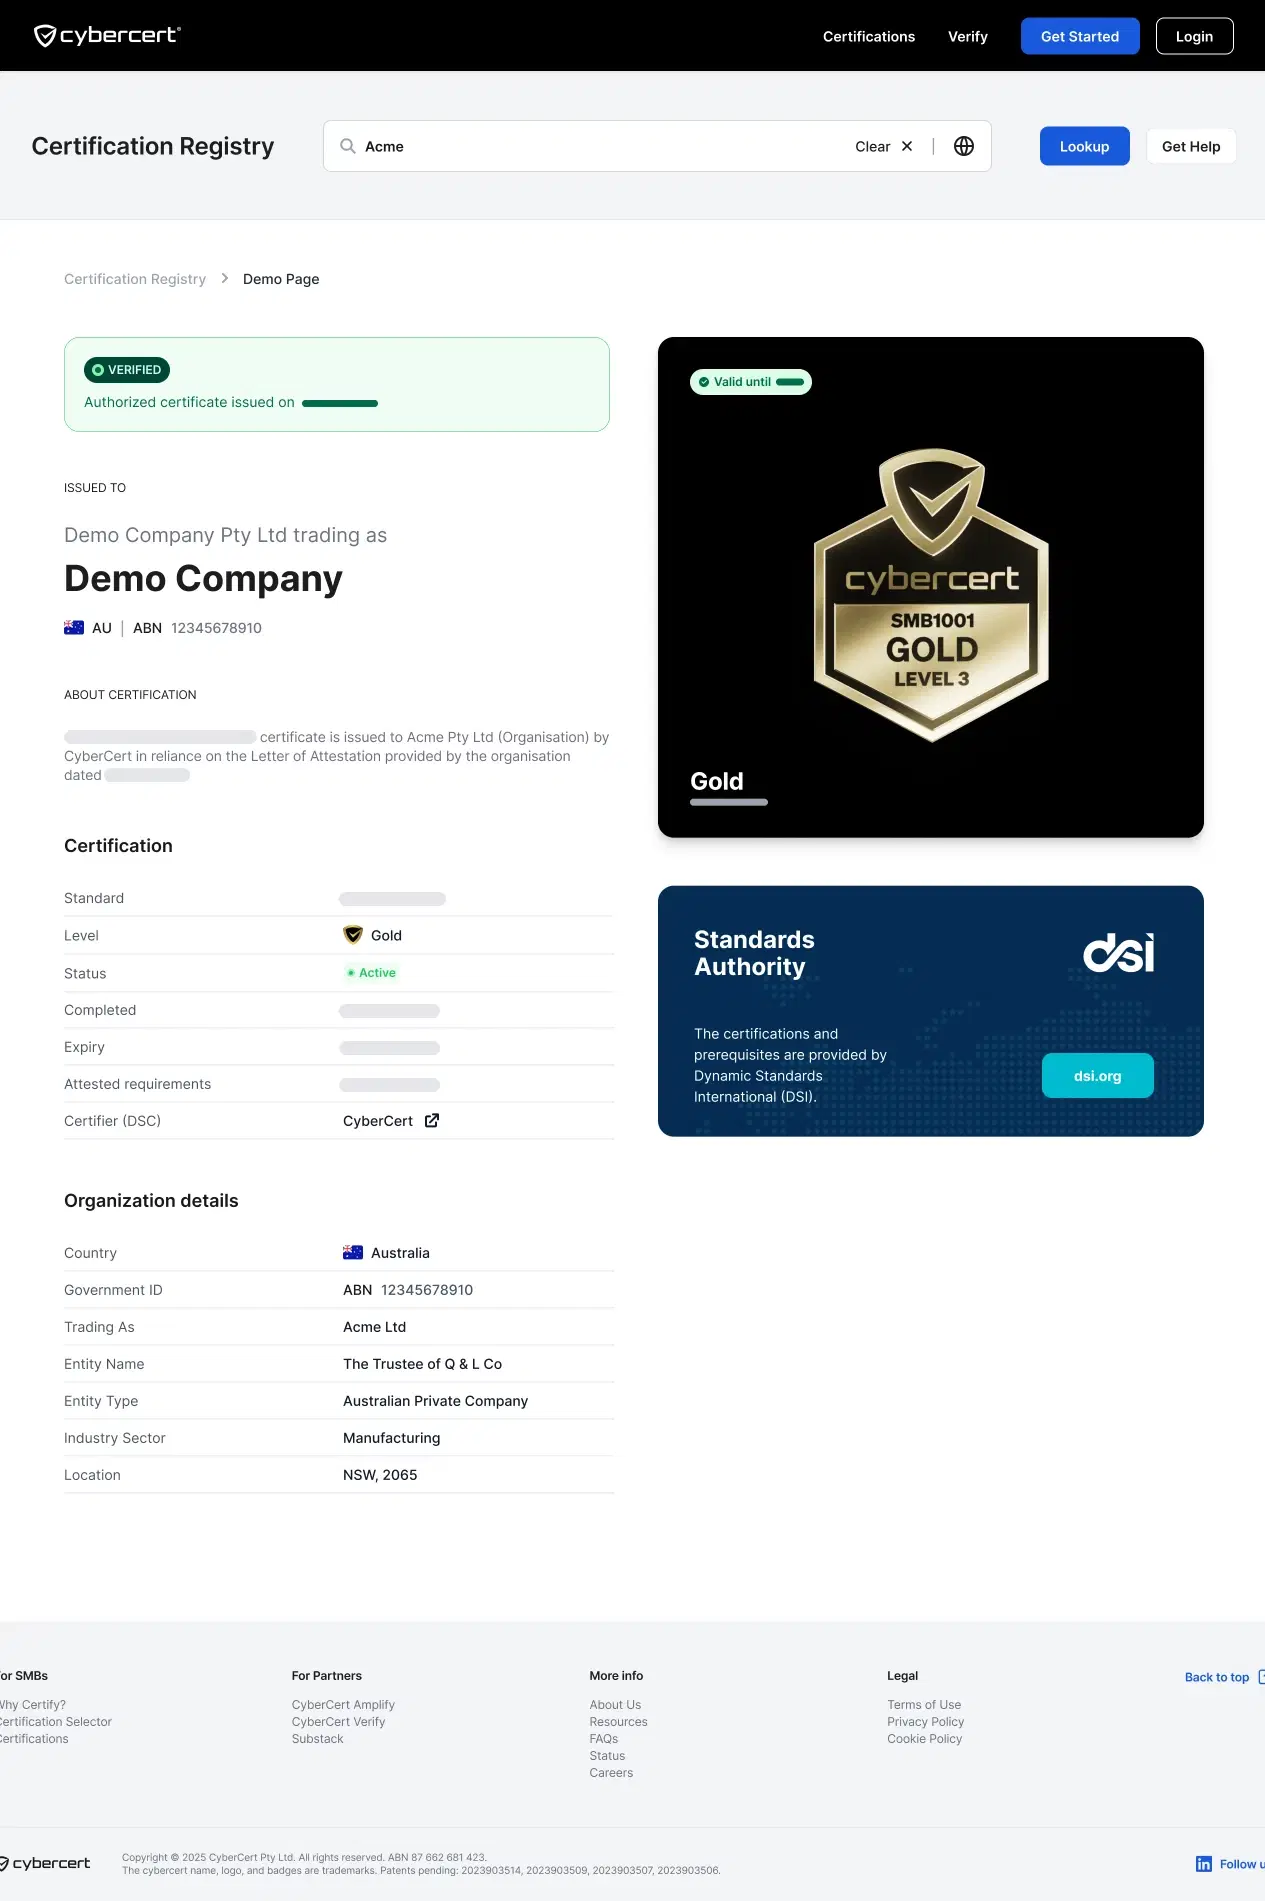
Live links to verify.cybercert.ai and dashboard.cybercert.ai to check and track supplier certification status in real time.
Insurance Integration
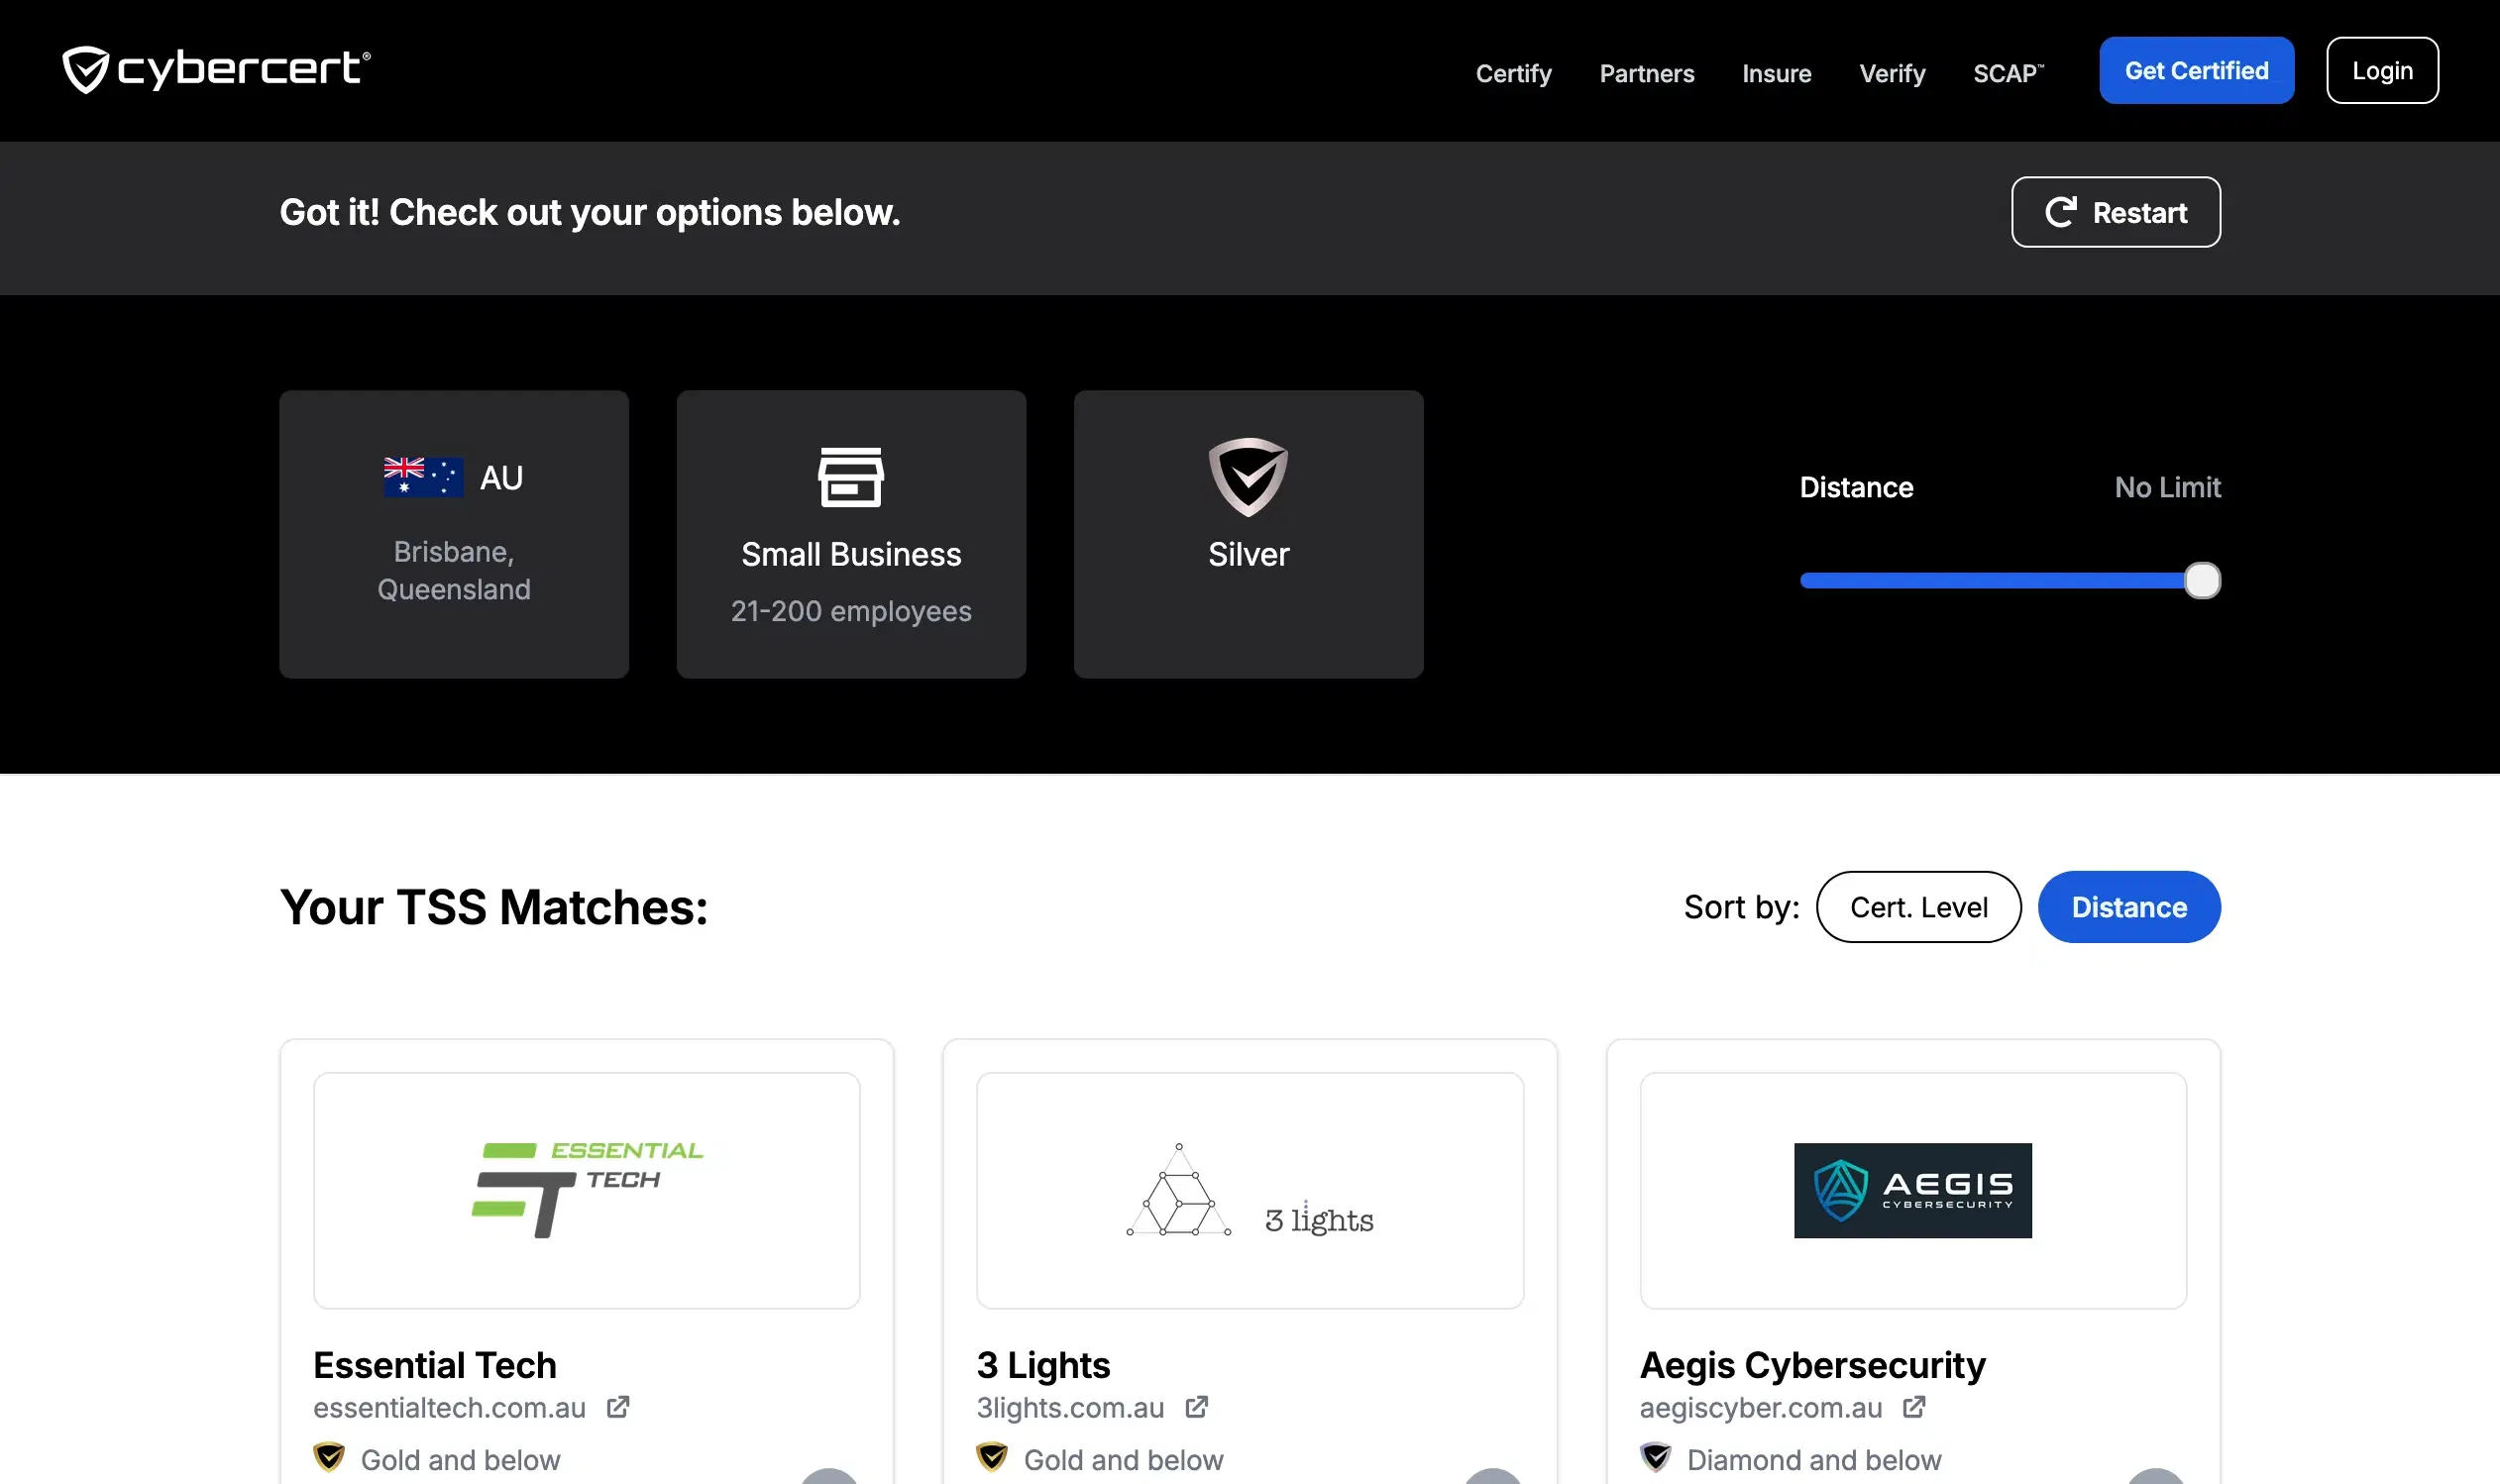
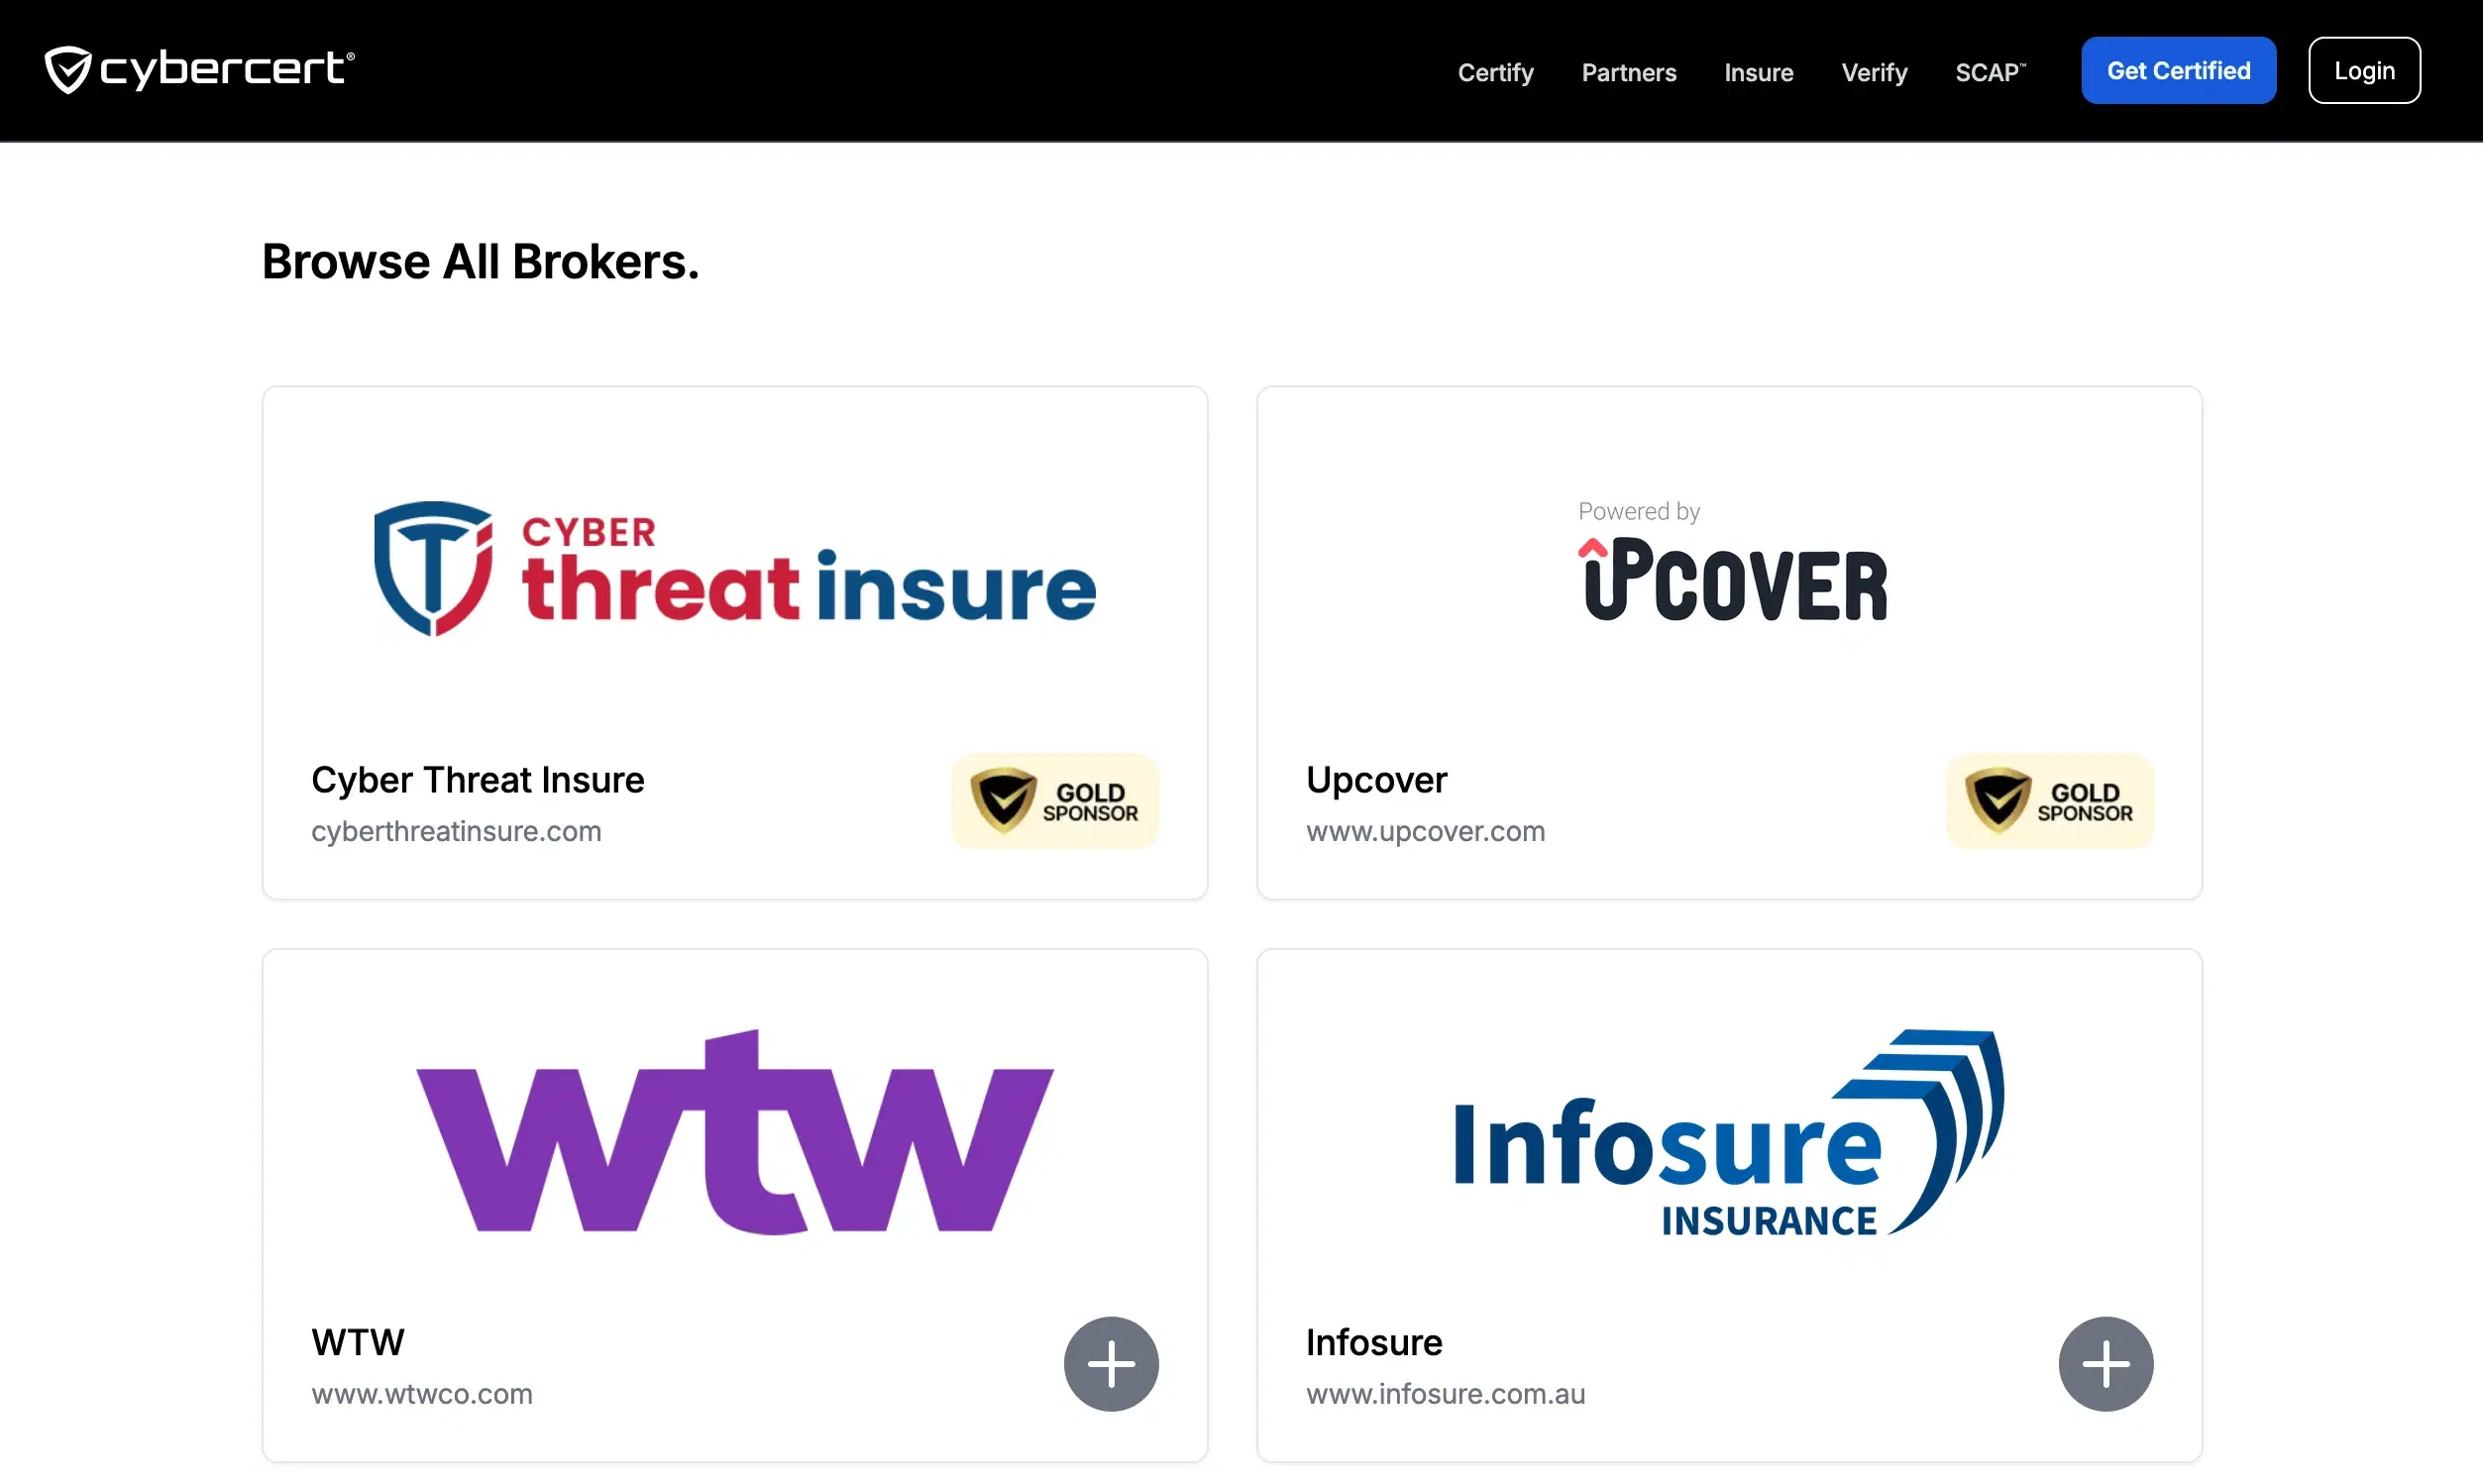
Built-in cyber insurance requirements and pathways — including sponsored Gold certification subscription credits for eligible insurer partners.
Disclaimer
General use
This SCAP™ Activation Toolkit is provided by CyberCert Pty Ltd for general informational and operational guidance. It is not a substitute for professional legal, cybersecurity, insurance, procurement, or risk-management advice. Use of this toolkit does not guarantee compliance with any law, standard, contractual obligation, or insurer requirement, nor does it eliminate cyber risk.
No warranty
The materials, templates, clauses, checklists, and tools are provided “as is” and “as available,” without warranties of any kind, express or implied, including accuracy, fitness for a particular purpose, or non-infringement. To the maximum extent permitted by law, CyberCert disclaims liability for any loss or damage arising from use of, or reliance on, this toolkit.
Currency
Cybersecurity standards, threats, and best practice evolve. Content reflects CyberCert’s view as at the publication date and may be superseded without notice.
Contract Clauses
The clauses in Section 4 are illustrative drafting examples only. They have not been prepared for any specific transaction, jurisdiction, supplier relationship, or regulatory regime. They are not legal advice and do not create a solicitor–client relationship. Before incorporating any clause into a contract you must obtain advice from qualified legal counsel admitted in the relevant jurisdiction. CyberCert accepts no responsibility for clauses that are adopted, modified, or rejected.
Sponsored Pathways & Cyber Insurance
References to cyber insurance, the CyberCert Insure pathway, sponsored Gold certifications, and insurer partners are informational only. They do not constitute insurance advice, a binding offer of cover, a recommendation, or a guarantee of eligibility.
Email Templates
The email templates in Section 5 are sample communications. Before sending you must: review for accuracy and tone, replace every merge field, verify supplier eligibility, and confirm compliance with applicable privacy, anti-spam, and electronic communications laws (e.g. Spam Act 2003 (Cth), GDPR, CAN-SPAM, as relevant). Templates that imply contractual consequences (suspension, termination, eligibility review) should be reviewed by legal and procurement before issue.
Third-party links and resources
This toolkit references third-party websites, frameworks, training programs, and tools (including dsi.org, partner technology providers, and insurer partners). CyberCert does not control and is not responsible for the content, accuracy, availability, security, or practices of third parties. Inclusion is for convenience and does not constitute endorsement.
Statistics and external data
Statistics in this toolkit, including figures attributed to the WEF Global Cybersecurity Outlook 2024, are drawn from third-party publications at a point in time. CyberCert has not independently verified the underlying methodology of these statistics. Refer to the original source for current data and full context.
No guarantee of cyber resilience
Implementation of the SCAP program, achievement of any SMB1001 tier, ISO/IEC 27001, SOC 2 attestation, or any combination of the above, reduces but does not eliminate the risk of cyber attack, data breach, supply-chain compromise, or operational disruption. No certification, framework, attestation, or insurance product can guarantee security outcomes.
Up next
Tier Classification
Launch Checklist
Step Detail
Nominate your SCAP™ program lead
Designating a clear owner is the most important first action — without an internal champion, the program stalls at the first point of resistance.
- Choose someone with cross-functional authority — procurement, risk management, or IT governance are natural fits.
- Give them a mandate to request supplier data and enforce compliance deadlines.
- Ensure they have access to this toolkit, your supplier register, and your contract templates.
Phased Program Detail
- Export your full supplier list from your ERP, procurement system, or accounts payable records.
- Classify each supplier as Tier 1 (Enterprise) — complex organisations typically 1,000+ staff — or Tier 2 (SMB).
- Assign a risk rating: High (sensitive data, mission-critical, privileged access), Medium (interacts with systems, not critical), or Low (no sensitive data, easily replaceable).
- Use the DSI Categorization Matrix at dsi.org/categorization-matrix to support classification decisions.
- Map each supplier to a required certification level — see Section 3 of this toolkit.
Up next
Contract Clauses
Tier 1 · Enterprise
ISO / SOC 2 Pathway
~5% of your Supplier
Cyber Risk Level
Tier 2 · SMB Suppliers
SMB1001 / CyberCert Pathway
~95% of your Supplier


ISO/IEC 27001 or SOC 2 Type II or equivalent. Plus: Supplier Cybersecurity Questionnaire on request.
Audit, remote assessment, or onsite verification at any time during contract.
HighHigh Cyber Risk


SMB1001 (Platinum/Diamond Tiers)
Handles sensitive/regulated data, mission-critical, or privileged system access. Cannot be substituted within 7 days.
Audit, remote assessment, or onsite verification. Remediation within agreed timeframe.

Supplier Cybersecurity Questionnaire. Controls maintained per ISO 27001 or NIST CSF governance model.
Random audits or assurance reviews.
MediumMedium Cyber Risk

SMB1001 (Gold Tier or above)
Interacts with systems/information but doesn't store regulated data. Substituted in 7–30 days.
Random audits or assurance reviews at discretion.
Annual cybersecurity attestation confirming basic safeguards (passwords, patching, antivirus, backups, MFA).
Spot-check audits at discretion.
LowLow Cyber Risk


SMB1001 (Bronze/Silver Tiers)
No access to sensitive data, not critical to continuity. Replaced in 30+ days without material impact.
Spot-check audits.
Alternatively: completed reduced cyber questionnaire.
Sponsored Pathways
Subsidized options for smaller suppliers.
SMB Size Guidance.
Employee count ranges to help suppliers find their recommended starting certification level.
Bronze
Baseline cyber hygiene for any business with an Internet connection.
Silver
Cyber-insurable. Enhanced security for businesses facing moderate risk.
Gold
Compliance Ready. Advanced measures for compliance-heavy industries.
Platinum
Hardened and Audited. Comprehensive controls for high-risk, critical sectors.
Diamond
Ecosystem Hardened and Audited. Most comprehensive controls for highest assurance.
Fewer than 20
 Bronze (L1)
 Up to Diamond depending on risk
20–99
 Silver (L2)
 Gold (L3)Up to Diamond depending on risk
100–249
Gold (L3)Diamond (L5)250–499
Gold (L3) Platinum (L4)Diamond (L5)
500+
Platinum (L4)Diamond (L5)Certification requirements.
Check out the requirements below to see what certification level your business may immediately qualify for.
Select Standard
Up next
Email Templates
Important:
These clauses are sample language for internal use only and are not legal advice. See full disclaimer at end of document. Review with your legal team before contractual use.
Contract Clauses
1. Purpose & Scope
This clause establishes the cybersecurity and information security obligations applicable to all Suppliers engaged by the Customer. It applies proportionally based on the Supplier's assigned risk category (High Risk, Medium Risk, or Low Risk), as determined by the Customer's risk assessment framework and supported by the DSI Categorization Matrix (dsi.org/categorization-matrix).
2. General Requirements (All Suppliers)
All Suppliers, regardless of tier, must:
a) Implement and maintain reasonable and proportionate cybersecurity measures to protect against unauthorised access, disclosure, loss, or compromise of Customer data.
b) Promptly notify the Customer of any actual or suspected cyber incident, data breach, or security compromise affecting services or data under this Agreement.
c) Cooperate fully with any Customer investigation, audit, or remediation activity related to cybersecurity.
d) Ensure subcontractors and affiliates engaged in delivery of the contracted services adhere to equivalent standards.
3a. Tier 1 Enterprise Suppliers: Risk-Based Certification
High Risk Enterprise Suppliers must demonstrate compliance with one of the following: ISO/IEC 27001 certification; SOC 2 Type II report; or an equivalent internationally recognised standard approved by the Customer. Must complete the Enterprise Supplier Cybersecurity Questionnaire on request and maintain updated responses throughout the contract term. May be subject to audit, remote assessment, or onsite verification at any time during the contract term and prior to service commencement. Must remediate any deficiencies within a mutually agreed timeframe.
Medium Risk Enterprise Suppliers must provide evidence of cybersecurity maturity by completing the Enterprise Supplier Cybersecurity Questionnaire. May be subject to random audits or assurance reviews. Must maintain controls in accordance with an industry standard governance model (e.g. ISO 27001, NIST CSF).
Low Risk Enterprise Suppliers must complete an annual cybersecurity attestation confirming implementation of basic safeguards (e.g. strong passwords, patching, antivirus, backups, MFA). May be subject to spot-check audits at the Customer's discretion.
3b. Tier 2 SMB Suppliers: Risk-Based Certification
High Risk SMB Suppliers must demonstrate compliance with Platinum or Diamond SMB1001 Certification issued by CyberCert, as defined in the DSI Categorization Matrix. May be subject to audit, remote assessment, or onsite verification at any time.
Medium Risk SMB Suppliers must hold a CyberCert Gold or higher SMB1001 Certification. May be subject to random audits or assurance reviews.
Low Risk SMB Suppliers must hold at minimum a CyberCert Bronze or Silver SMB1001 Certification, or alternatively provide a completed reduced set of cyber questions as provided by the Customer. May be subject to spot-check audits at the Customer's discretion.
4. Evidence & Verification
Suppliers must provide current certificates, attestations, or completed questionnaires within ten (10) business days of request.
Failure to maintain compliance with these obligations, or refusal to provide evidence, may constitute a material breach of contract and grounds for suspension or termination.
The Customer reserves the right to verify certification status at any time via the CyberCert certification registry at verify.cybercert.ai.
5. Continuous Improvement
The Customer and Supplier acknowledge that cybersecurity standards and threats evolve. Suppliers shall review and update their security controls and certifications annually or as required to remain aligned with current best practice and the SMB1001 standard or its successors.
Disclaimer
General use
This SCAP™ Activation Toolkit is provided by CyberCert Pty Ltd for general informational and operational guidance. It is not a substitute for professional legal, cybersecurity, insurance, procurement, or risk-management advice. Use of this toolkit does not guarantee compliance with any law, standard, contractual obligation, or insurer requirement, nor does it eliminate cyber risk.
No warranty
The materials, templates, clauses, checklists, and tools are provided “as is” and “as available,” without warranties of any kind, express or implied, including accuracy, fitness for a particular purpose, or non-infringement. To the maximum extent permitted by law, CyberCert disclaims liability for any loss or damage arising from use of, or reliance on, this toolkit.
Currency
Cybersecurity standards, threats, and best practice evolve. Content reflects CyberCert’s view as at the publication date and may be superseded without notice.
Contract Clauses
The clauses in Section 4 are illustrative drafting examples only. They have not been prepared for any specific transaction, jurisdiction, supplier relationship, or regulatory regime. They are not legal advice and do not create a solicitor–client relationship. Before incorporating any clause into a contract you must obtain advice from qualified legal counsel admitted in the relevant jurisdiction. CyberCert accepts no responsibility for clauses that are adopted, modified, or rejected.
Sponsored Pathways & Cyber Insurance
References to cyber insurance, the CyberCert Insure pathway, sponsored Gold certifications, and insurer partners are informational only. They do not constitute insurance advice, a binding offer of cover, a recommendation, or a guarantee of eligibility.
Email Templates
The email templates in Section 5 are sample communications. Before sending you must: review for accuracy and tone, replace every merge field, verify supplier eligibility, and confirm compliance with applicable privacy, anti-spam, and electronic communications laws (e.g. Spam Act 2003 (Cth), GDPR, CAN-SPAM, as relevant). Templates that imply contractual consequences (suspension, termination, eligibility review) should be reviewed by legal and procurement before issue.
Third-party links and resources
This toolkit references third-party websites, frameworks, training programs, and tools (including dsi.org, partner technology providers, and insurer partners). CyberCert does not control and is not responsible for the content, accuracy, availability, security, or practices of third parties. Inclusion is for convenience and does not constitute endorsement.
Statistics and external data
Statistics in this toolkit, including figures attributed to the WEF Global Cybersecurity Outlook 2024, are drawn from third-party publications at a point in time. CyberCert has not independently verified the underlying methodology of these statistics. Refer to the original source for current data and full context.
No guarantee of cyber resilience
Implementation of the SCAP program, achievement of any SMB1001 tier, ISO/IEC 27001, SOC 2 attestation, or any combination of the above, reduces but does not eliminate the risk of cyber attack, data breach, supply-chain compromise, or operational disruption. No certification, framework, attestation, or insurance product can guarantee security outcomes.
Up next
Tracking Tools
Merge fields to customise:
Replace all [fields] with your organisation's details before sending. These include organisation name, contact mailbox, deadline dates, and supplier names.
Flow 1 — Initial Announcement
Part 1 · Silver Suppliers
Flow 2 — Reminder / Nudge
Send 2–3 weeks before deadline
Flow 3 — Escalation
Final week before deadline
Flow 4 — Confirmation of Compliance
Send once verified in dashboard / verify.cybercert.ai
Flow 5— Gold+ Initial Announcement
Part 2 · High-risk suppliers requiring Gold or above
Disclaimer
General use
This SCAP™ Activation Toolkit is provided by CyberCert Pty Ltd for general informational and operational guidance. It is not a substitute for professional legal, cybersecurity, insurance, procurement, or risk-management advice. Use of this toolkit does not guarantee compliance with any law, standard, contractual obligation, or insurer requirement, nor does it eliminate cyber risk.
No warranty
The materials, templates, clauses, checklists, and tools are provided “as is” and “as available,” without warranties of any kind, express or implied, including accuracy, fitness for a particular purpose, or non-infringement. To the maximum extent permitted by law, CyberCert disclaims liability for any loss or damage arising from use of, or reliance on, this toolkit.
Currency
Cybersecurity standards, threats, and best practice evolve. Content reflects CyberCert’s view as at the publication date and may be superseded without notice.
Contract Clauses
The clauses in Section 4 are illustrative drafting examples only. They have not been prepared for any specific transaction, jurisdiction, supplier relationship, or regulatory regime. They are not legal advice and do not create a solicitor–client relationship. Before incorporating any clause into a contract you must obtain advice from qualified legal counsel admitted in the relevant jurisdiction. CyberCert accepts no responsibility for clauses that are adopted, modified, or rejected.
Sponsored Pathways & Cyber Insurance
References to cyber insurance, the CyberCert Insure pathway, sponsored Gold certifications, and insurer partners are informational only. They do not constitute insurance advice, a binding offer of cover, a recommendation, or a guarantee of eligibility.
Email Templates
The email templates in Section 5 are sample communications. Before sending you must: review for accuracy and tone, replace every merge field, verify supplier eligibility, and confirm compliance with applicable privacy, anti-spam, and electronic communications laws (e.g. Spam Act 2003 (Cth), GDPR, CAN-SPAM, as relevant). Templates that imply contractual consequences (suspension, termination, eligibility review) should be reviewed by legal and procurement before issue.
Third-party links and resources
This toolkit references third-party websites, frameworks, training programs, and tools (including dsi.org, partner technology providers, and insurer partners). CyberCert does not control and is not responsible for the content, accuracy, availability, security, or practices of third parties. Inclusion is for convenience and does not constitute endorsement.
Statistics and external data
Statistics in this toolkit, including figures attributed to the WEF Global Cybersecurity Outlook 2024, are drawn from third-party publications at a point in time. CyberCert has not independently verified the underlying methodology of these statistics. Refer to the original source for current data and full context.
No guarantee of cyber resilience
Implementation of the SCAP program, achievement of any SMB1001 tier, ISO/IEC 27001, SOC 2 attestation, or any combination of the above, reduces but does not eliminate the risk of cyber attack, data breach, supply-chain compromise, or operational disruption. No certification, framework, attestation, or insurance product can guarantee security outcomes.
Download the SCAP™ Playbook.Risk-Based 2-Tier Model.